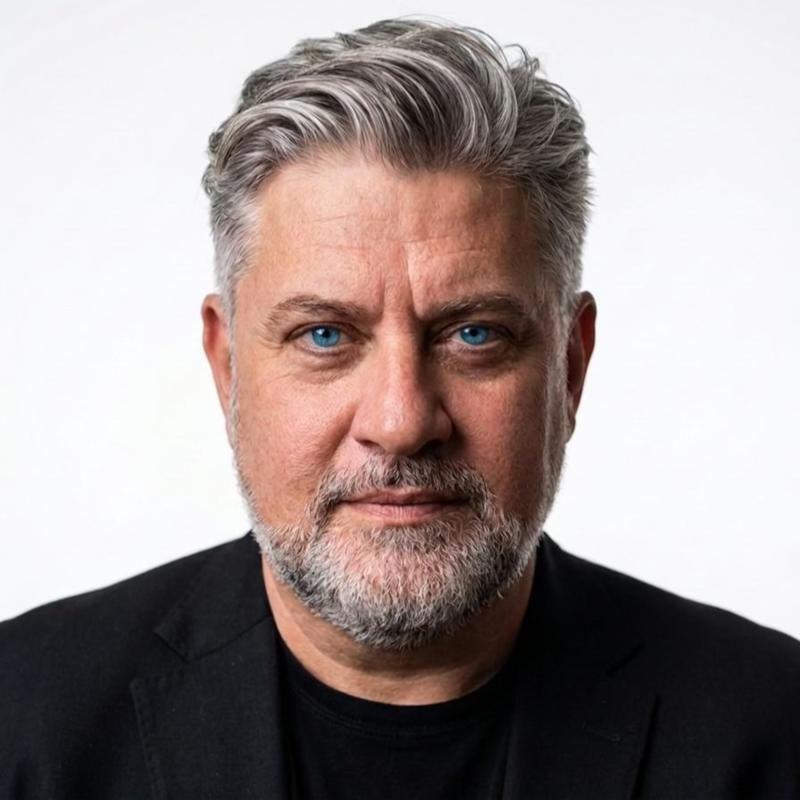
An occasional blogger… I am an experienced consultant in cybersecurity, digital forensics and ICT legal compliance, with more than 24 years of experience working in critical environments for a wide range of clients, including the banking sector. My passion for cybersecurity and IT governance has led me to keep exploring the dynamics and challenges of the digital world.
Throughout my career, I have worked with businesses, governments and international organisations to help protect their sensitive data and manage constantly evolving cyber threats.
I am the author of several bestselling books published in four languages on Amazon, including the following. The titles below are translated into English for reference; the links lead to the original editions. The books are available on Amazon in four languages: Italian, Spanish, French and English.
- Compliance Without Illusions: Turning PCI DSS, ISO 27001 and NIS2 into Real, Practical, Auditable and Sustainable Controls (Law and Technology: European Compliance in the Digital Landscape) https://www.amazon.it/dp/B0GJ6MXCGC
- NIS2 (EU) 2022/2555 Compliance Framework: A Guide to Understanding and Implementing NIS2, with an Operational Toolkit and ITIL Guidance for Indicators and Dashboards (Law and Technology: European Compliance in the Digital Landscape) https://www.amazon.it/dp/B0FRRFNDVB
- The DORA Code, Regulation (EU) 2022/2554: A 2025 Practical Guide to European Digital Resilience (Law and Technology: European Compliance in the Digital Landscape) https://www.amazon.it/dp/B0F5SBM5SW
- A Guide to the Data Act (EU 2023/2854): A Practical Handbook for IT and Legal Professionals, Covering Obligations, Penalties and a Compliance Roadmap (Law and Technology: European Compliance in the Digital Landscape) https://www.amazon.it/dp/B0FD8FKHT4
- MiCA (EU) 2023/1114, Markets in Crypto-Assets: A Complete Practical Implementation Guide (Law and Technology: European Compliance in the Digital Landscape) https://www.amazon.it/dp/B0FL1MSYZK
From early 2022 to the end of 2025, I served as an external Chief Information Security Officer (CISO) for a company in France whose identity remains confidential, managing cybersecurity and security architecture across the organisation.
Selected clients and significant projects (excluding my current client, whose identity remains confidential):
- DEXIA Bank: Served as Chief Information Security Officer (CISO) in a transition management role for four years.
- AXA Partners: Provided advice to strengthen cybersecurity and resilience against cyber threats. Implemented advanced safeguards for customer data and business operations.
- GSK: Developed security architectures to protect sensitive healthcare data in databases formerly held by Pfizer. Ensured compliance with European regulations through appropriate policies and procedures.
- Collection Pinault Paris – Bourse de Commerce: Designed and implemented the cyber and ICT security architecture, the Security Operations Centre (SOC) and its governance. Co-ordinated cybersecurity activities during the museum’s transition to its target infrastructure.
- ADP: Managed upgrades to European data centre infrastructure and corporate databases. Implemented security-by-design solutions to improve the reliability of ICT operations.
- IBM: Advised on digital forensics techniques to identify and respond to specific cyber threats.
- AREVA: Implemented cybersecurity solutions for critical nuclear energy infrastructure across engineering, production and maintenance.
- Société Générale: Designed and implemented cybersecurity measures for the analysis of structural vulnerabilities as part of the merger with Crédit du Nord.
- BNP Paribas: Advised on interoperability and cybersecurity architectures for local branches in France and as part of the merger with Italy’s BNL.
Expertise:
- CISO services and corporate governance.
- ITIL: IT service management and continual improvement.
- Change management: implementing effective organisational change.
- GDPR, DORA and NIS2: compliance with European data protection and information security regulations and directives.
- ISO 27001 and ISO 31000: international standards for information security management and risk management.
- NIST Cybersecurity Framework: CSF Certified.
Through this blog, I aim to share my knowledge, the latest developments and good practice in cybersecurity and information technology more broadly.
I am pleased to offer advice, insights and useful resources to help you understand the challenges and solutions in the ever-changing digital security landscape, in a straightforward, readable space without intrusive or misleading advertising.
I believe that education and awareness are essential to tackling cyber threats effectively and working towards a safe digital environment for individuals, businesses and institutions.
Raffaele Di Marzio, Senior Advisor in Cybersecurity, Forensics and Legal Compliance
https://www.linkedin.com/in/raffaeledimarzio
https://x.com/technocraticum